Compliance & Governance Software Solutions
We help compliance officers, CISOs, GRC teams, and regulated enterprises modernize policy management, audit automation, and risk operations with AI-powered, regulator-ready software built for the realities of multi-jurisdiction governance.
TRUSTED. CERTIFIED. PROVEN.


$203B
GRC Market by 2033
19.2%
RegTech CAGR
300+
Global Frameworks
50%
GRC Spend Increase
Engineering Built for Regulated Enterprises
Six advantages that come standard with every ZAPTA compliance and governance engagement combining deep regulatory domain expertise with modern AI engineering.
DOMAIN DEPTH
Compliance-Native Engineers
Our teams have shipped systems for banks, insurers, healthcare, energy, and government. They speak NIST, ISO 27001, SOC 2, GDPR, HIPAA, DORA, MiFID II, and SOX not generic workflow tools repurposed for compliance.
STAKEHOLDER FOCUSED
Built for the Three Lines of Defense
Risk owners, compliance teams, internal audit, and the board each see the system through different eyes. Every architectural decision starts with how each line of defense actually works not just where data lives.
AUDIT-READY
Evidence Produced as a Continuous Output
Audit trails, evidence capture, and control attestations generated by the system not assembled by hand at quarter-end. Regulators and external auditors get machine-readable artifacts on demand.
TIME-TO-MARKET
From Spreadsheet Chaos to Platform in Weeks
Cloud-native foundations, configurable control libraries, and AI-assisted engineering ship pilots in 8–14 weeks. Compare that to typical GRC implementations stretching 12–24 months for the same scope.
INTEROPERABILITY
One Truth Across Risk, Policy, and Controls
ServiceNow GRC, MetricStream, Archer, OneTrust, and custom systems integrated into a unified data model. We don't add another silo we wire your existing stack into a coherent whole.
OWNERSHIP
100% IP Stays With You
Source code, ML models, control libraries, and documentation transfer fully on day one. No vendor lock-in, no per-control surcharges, no renegotiation when you scale into new frameworks or jurisdictions.
 DOMAIN DEPTH
Compliance-Native Engineers
Our teams have shipped systems for banks, insurers, healthcare, energy, and government. They speak NIST, ISO 27001, SOC 2, GDPR, HIPAA, DORA, MiFID II, and SOX not generic workflow tools repurposed for compliance.

 STAKEHOLDER FOCUSED
Built for the Three Lines of Defense
Risk owners, compliance teams, internal audit, and the board each see the system through different eyes. Every architectural decision starts with how each line of defense actually works not just where data lives.
 AUDIT-READY
Evidence Produced as a Continuous Output
Audit trails, evidence capture, and control attestations generated by the system not assembled by hand at quarter-end. Regulators and external auditors get machine-readable artifacts on demand.
 TIME-TO-MARKET
From Spreadsheet Chaos to Platform in Weeks
Cloud-native foundations, configurable control libraries, and AI-assisted engineering ship pilots in 8–14 weeks. Compare that to typical GRC implementations stretching 12–24 months for the same scope.
 INTEROPERABILITY
One Truth Across Risk, Policy, and Controls
ServiceNow GRC, MetricStream, Archer, OneTrust, and custom systems integrated into a unified data model. We don't add another silo we wire your existing stack into a coherent whole.
 OWNERSHIP
100% IP Stays With You
Source code, ML models, control libraries, and documentation transfer fully on day one. No vendor lock-in, no per-control surcharges, no renegotiation when you scale into new frameworks or jurisdictions.
Compliance & Governance Software Services
Nine core service lines each delivered as standalone engagements or as part of a full GRC platform build.


Discovery & GRC Strategy
Regulatory mapping, control framework design, target operating model, and reference architecture. Output: fixed-scope proposal in 48 hours.
 View details
Contact to learn more

Policy & Control Platforms
Custom policy management, control libraries, attestation workflows, and exception handling. Built on cloud-native foundations and tied directly to evidence collection from day one.
View details
Contact to learn more

Regulatory Change Management
Real-time horizon scanning, regulatory feed ingestion, impact assessment, and obligation mapping. Built to track 300+ global frameworks against your business and surface what actually matters.
View details
Contact to learn more

AI Compliance Copilots
GenAI assistants for policy drafting, regulatory Q&A, control narrative review, and audit response. Trained on your obligations library with explainability and human-in-the-loop oversight.
View details
Contact to learn more

Audit & Evidence Automation
Continuous controls monitoring, automated evidence capture, walkthrough scheduling, and audit workpaper generation. Internal audit and external attestation become a documentation exercise not a quarterly fire drill.
View details
Contact to learn more

Third-Party & Vendor Risk
Vendor onboarding, due diligence, ongoing monitoring, contract risk scoring, and TPRM workflows. Plus integration with vendor questionnaire libraries (CAIQ, SIG) and threat intelligence feeds.
View details
Contact to learn more

Data Privacy & DSAR Engineering
GDPR, CCPA, and global privacy program engineering RoPA, consent management, DSAR fulfillment automation, and data discovery across structured and unstructured systems.
View details
Contact to learn more

Legacy GRC Modernization
Phased migration off spreadsheet-driven processes, aging on-premise GRC, and bespoke compliance systems. Strangler-fig patterns and zero-downtime cutovers with audit continuity preserved.
View details
Contact to learn more

Continuous Controls & SRE
Automated control testing, observability for compliance posture, real-time risk dashboards, and 24/7 SRE turning compliance into a continuous operational discipline rather than a periodic event.
View details
Contact to learn more
Need just one of these? Or a full platform build? Both work let's scope.
Or a full platform build? Both work let's scope.
Discuss Your ProjectThe Outcomes That Matter
Six outcomes our compliance and governance clients consistently realize the ones that move regulator confidence, audit cycle time, and risk posture in the right direction.
 01
Audit Cycle Time Compresses
Evidence collection that used to consume weeks happens continuously in the background. Auditors arrive to a system that already has the answers. Quarter-end stops being a fire drill.
 02
Compliance Teams Focus on Judgment
Routine attestation, evidence routing, and regulatory tracking move into the platform. Compliance officers spend their time on the calls that need human judgment not on chasing screenshots and signatures.
 03
Risk Visibility Across the Enterprise
Risk owners, second-line teams, and executives see the same picture at the same time, in the same format. Surprises stop showing up in board reports because they surface in the dashboard first.
 04
Regulatory Change Lands Faster
New rules, amendments, and guidance flow into the obligations library, get mapped to controls, and trigger remediation tasks automatically. Time from regulator publication to operational response shrinks.
 05
Vendor & Third-Party Risk Stays Current
Vendor risk stops being a once-a-year questionnaire. Continuous monitoring, contract intelligence, and threat feeds keep the third-party portfolio accurate between formal reviews and through the year-end push.

Trust That Survives Examination Day
Platforms designed to satisfy SOC 2, ISO 27001, NIST, GDPR, HIPAA, DORA, and sector regulators from the architecture stage. Examinations become a documentation exercise not an existential event.
Get a free consultationWhat We Build For Compliance & Governance Teams
Concrete use cases we've shipped across GRC and RegTech each a real product scenario, not a service category.

Policy Management Platforms
Centralized policy lifecycle management with audit-ready evidence and control framework integration.


-
 Centralized policy drafting and review workflows that streamline collaboration across every stakeholder involved
-
Approval and distribution tools that ensure every policy reaches the right people on time
-
Approval and distribution tools that ensure every policy reaches the right people on time
-
Attestation tracking that confirms every employee has read and acknowledged required policy updates
-
Exception handling workflows that document, approve, and track every policy deviation transparently

Regulatory Change Tracking
Real-time regulatory horizon scanning across 300+ global frameworks with automated impact assessment.
-
Real-time regulatory horizon scanning across 300+ global frameworks with automated impact assessment.
-
Auto-classification of new rules that categorizes and prioritizes every regulatory update automatically
-
Impact assessment workflows that evaluate how every new regulation affects your existing controls
-
Obligation-to-control mapping that links every regulatory requirement to the right internal control owner
-
Eliminates the need for compliance teams to manually monitor dozens of regulatory newsletters weekly
Third-Party & Vendor Risk Management
End-to-end vendor risk platform covering onboarding, monitoring, and offboarding with full integration.
-
Vendor onboarding workflows that capture due diligence requirements before any engagement begins
-
Continuous monitoring that tracks vendor risk posture changes throughout the entire relationship lifecycle
-
Contract risk scoring that identifies and flags high-risk clauses and obligations automatically
-
Structured offboarding that ensures clean, compliant, and documented vendor relationship terminations every time
-
CAIQ and SIG questionnaire library integration with live security ratings feeds for comprehensive vendor oversight
Privacy & DSAR Automation
Automated privacy workflows covering DSAR, consent, and breach notification for global compliance.
-
Automated DSAR workflows that capture, process, and fulfill data subject requests within regulatory deadlines
-
Consent management tools that collect, store, and honor user preferences across every digital touchpoint
-
Records of Processing Activities that maintain an accurate and always audit-ready data inventory
-
Breach notification workflows that ensure timely and regulator-compliant incident reporting every time
-
Data discovery across structured and unstructured systems built for GDPR, CCPA, and global privacy regimes

AI Governance & Model Risk
AI inventory and model risk workflows built for NIST, ISO 42001, and EU AI Act.
-
AI inventory management that maintains a complete and current registry of every deployed model
-
Model cards and bias testing that ensure every AI system is transparent and fair
-
Ongoing model monitoring that detects performance degradation and unexpected behavioral drift early
-
AI use-case approval workflows that govern every new deployment with structured oversight
-
Built to satisfy NIST AI RMF, ISO 42001, EU AI Act, and emerging sectoral guidance

Internal Audit & Evidence Collection
Risk-based audit management with automated workpapers built for SOX and attestation programs.
-
Audit universe management that maintains a complete and prioritized view of every auditable entity
-
Risk-based audit planning that focuses resources on the highest-impact areas first
-
Automated workpaper generation that eliminates manual documentation and accelerates audit fieldwork significantly
-
Finding tracking that ensures every audit issue is assigned, monitored, and resolved on time
-
Remediation workflows built for internal audit, SOX compliance, and external attestation programs

Whistleblower & Ethics Platforms
Confidential intake and case management built for EU Directive and SOX 806 compliance.
-
Confidential intake channels that give employees a safe and anonymous reporting mechanism always
-
Case management workflows that organize, assign, and track every ethics report systematically
-
Structured investigation workflows that ensure every concern is handled consistently and fairly
-
Analytics that surface patterns and trends across ethics reports before issues escalate further
-
Built to satisfy EU Whistleblower Directive, SOX 806, and sector-specific ethics reporting requirements

ESG & Sustainability Reporting
Continuous ESG data collection and reporting built for GRI, SASB, TCFD, and CSRD.
-
Carbon accounting tools that measure and track emissions across operations and entire supply chains
-
Supply chain disclosure workflows that capture and verify vendor sustainability data at scale
-
GRI, SASB, TCFD, and CSRD reporting built directly from live operational system data
-
Assurance evidence collection that keeps sustainability reports audit-ready and regulator-compliant at all times
-
Continuous data collection that eliminates the annual sustainability-team scramble before reporting deadlines

SOX Controls & Financial Reporting
ICFR control libraries and automated testing built for SOX compliance and quarterly certifications.
-
ICFR control libraries that organize and maintain every financial reporting control in one place
-
Walkthrough scheduling that keeps SOX testing on track across every business unit and cycle
-
Automated evidence capture that reduces manual effort and accelerates control testing significantly
-
Deficiency tracking that ensures every control gap is documented, remediated, and closed on time
-
ERP audit log integration that enables automated control testing across financial reporting systems

AML, KYC & Sanctions Orchestration
-
Customer onboarding workflows that capture and verify KYC requirements before any relationship begins
-
Transaction monitoring that detects suspicious activity patterns across every customer account continuously
-
Sanctions screening and PEP checks that flag high-risk individuals and entities in real time
-
SAR and STR filing workflows that ensure timely and accurate regulatory submissions every time
-
Case management and quality assurance tools built for AML investigation teams at any scale

Operational Resilience & DORA
Critical function mapping and ICT risk management built for DORA and OpRes mandates.
-
Critical function mapping that identifies and documents every operationally important business process
-
ICT risk register that tracks every technology risk across the entire operational environment
-
Third-party concentration analysis that flags dangerous dependencies on single vendors or providers
-
Incident reporting workflows that ensure timely and regulator-compliant operational disruption notifications
-
Threat-led penetration testing programs built to satisfy DORA, FFIEC, and OpRes mandate requirements

Cyber Risk Quantification
FAIR-based cyber risk modeling and quantified scenarios built for board-level risk reporting.
-
FAIR-based cyber risk modeling that translates technical threats into quantified financial impact scenarios
-
Control-coverage analytics that identify gaps and prioritize cybersecurity investments by measurable risk reduction
-
Quantified risk scenarios that give boards and executives clear and actionable cyber risk visibility
-
Integration with vulnerability scanners, SIEM, and threat intelligence feeds for continuous risk updates
-
Board-level reporting that communicates cyber exposure in business terms rather than technical jargon

Audit Analytics & Continuous Auditing
Continuous auditing pipelines and anomaly detection that surface issues between formal audit cycles.
-
Transaction analytics that continuously scan financial data for errors, fraud, and policy violations
-
Expense report monitoring that flags anomalies and policy exceptions before they become larger issues
-
Master data analytics that detect duplicate, incomplete, or unauthorized changes across critical data sets
-
Anomaly detection and exception reporting that prioritize the highest-risk findings for auditor review
-
Continuous auditing pipelines that keep audit coverage active between formal scheduled audit cycles

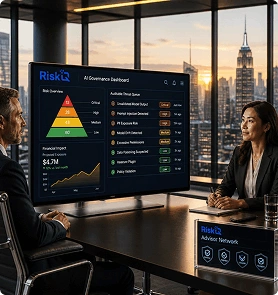
Executive & Board Risk Dashboards
Live risk appetite and KRI dashboards generated directly from underlying GRC system data.
-
Risk appetite tracking that shows executives exactly where the organization stands against defined thresholds
-
KRI dashboards that surface leading indicators before risks escalate into material issues or incidents
-
Regulatory exam readiness scores that give leadership real-time visibility into compliance posture always
-
Audit committee reporting generated directly from underlying GRC data without manual assembly required
-
Eliminates last-minute PowerPoint scrambles by delivering board-ready insights from live system data
Recent Compliance & Governance Engagements
Six representative projects across financial services, healthcare, technology, and regulated enterprises.
Content Platform Redesign
How ZAPTA helped redesign and rebuild the V3 experience for a leading content-repurposing platform, bringing clarity, consistency, and a unified design system across every module of a product trusted by 980K+ creators.
Digital Identity Verification App
How ZAPTA delivered a secure digital identity and contact management mobile app that keeps users’ details verified and up to date in real time, launched across Denmark and the USA with 5,000+ verified users

FinTech Trade & Financing Platform
Founder with a clear vision shipped a multi-tenant SaaS platform in 12 weeks auth, billing, dashboards, and core workflows. Live customers within 90 days.
Healthcare Onboarding Platform
How ZAPTA helped a healthcare organization replace a manual, fragmented hiring process with a unified, compliance-ready onboarding platform, bringing applicants, employees, referees, and administrators into a single role-based system.
Property Management Platform
How ZAPTA helped a property management company replace fragmented manual operations with a single platform connecting tenants, vendors, and property owners, with 20,000+ properties listed across 10 US states.

Smart POS Platform
How ZAPTA helped a technology company build a SaaS point-of-sale platform that unifies sales, inventory, and payments with real-time analytics and full online and offline functionality, built for the Saudi market across four sectors.

Ticketing Analytics Platform
How ZAPTA built a real-time analytics and ticketing-insights platform that reveals pricing trends and optimal purchase timing, helping buyers across 100+ locations purchase 15K+ tickets and save over $100K.
Unified GRC Platform
How ZAPTA helped deliver a unified governance, risk, and compliance platform that automates compliance, risk, and legislative tracking, cutting regulatory-change monitoring time by 40% and audit preparation by 35%.

AI EdTech Platform
How ZAPTA helped an EdTech client turn traditional tutoring into a personalized, AI-driven experience, intelligently matching students with suitable tutors, with 1,500 students enrolled and 591+ expert tutors on the platform.
Where Our Compliance & Governance Depth Runs Deepest
Six regulated verticals where we bring shipped-product experience and named-engineer expertise.

Financial Services Compliance

AML, KYC, transaction monitoring, MiFID II, EMIR, Basel, DORA, SR 11-7 model risk, and FFIEC. For banks, broker-dealers, asset managers, and digital banks operating across regulated jurisdictions.

Healthcare & Life Sciences GRC
HIPAA, HITECH, FDA 21 CFR Part 11, GxP, ISO 13485, and HITRUST. For health systems, payers, pharma, and medical device companies navigating clinical, privacy, and quality regulatory regimes.

Tech & SaaS Compliance
SOC 2 Type II, ISO 27001, ISO 27701, FedRAMP, PCI DSS, and HITRUST. For SaaS scale-ups and tech enterprises operating in multiple customer compliance contexts simultaneously.

Energy & Critical Infrastructure
NERC CIP, ISO 27019, IEC 62443, TSA pipeline directives, and supply-chain security mandates. For utilities, oil and gas, power generation, and industrial operators with OT and IT obligations.

Public Sector & Government
NIST 800-53, FISMA, FedRAMP, CMMC, IRAP, and regional government frameworks. For agencies, contractors, and managed service providers operating in classified and controlled environments.

ESG & Sustainability Programs
GRI, SASB, TCFD, CSRD, ISSB, and regional carbon disclosure. For enterprises operationalizing sustainability programs across reporting, supply chain, and assurance workflows at portfolio scale.
Our Three-Phase Delivery Process
Same process for every engagement. Different durations. Full builds: 12–20 weeks. Pilots and integrations: 6–10 weeks.
Consult & Align

-
- Stakeholder workshops
- Regulatory & compliance mapping
- Reference architecture
- Risk register & success metrics
- Fixed-scope proposal

Discovery, regulatory mapping, and scope. Output: fixed-scope proposal in 48 hours.
Design & Engineer
-
- Figma UX & design system
- Cloud-native engineering
- Core systems integrations
- Automated test pipelines
- Weekly demos & feedback

UX, architecture, build, and continuous evaluation with weekly working demos.
Deploy & Evolve
-
- Zero-downtime deployment
- Production observability
- Performance & cost tuning
- Performance & cost tuning
- Optional engineering retainer

Cloud deployment, observability, and ongoing iteration as your business scales.
Want this process applied to your compliance program? Get a roadmap in 24 hours.
We'll share a roadmap within a couple of working days.
Start Your ProjectOur Compliance & Governance Technology Stack
Modern, regulator-ready tools chosen for your control, evidence, and reporting requirements.



ISO 9001:2015 certified quality software engineering
Top-rated AI & custom software development company

Recognized leader in building AI-powered software and solutions.

Globally recognized for top custom software development

Most reviewed partner for AI and software solutions

Verified experts in premium custom software development

Top-ranked in delivering MVP development services

Ranked among global innovators for SaaS and SMEs software
Award-winning partner for scalable web and mobile app projects
Top-ranked firm in web and mobile app development
Compliance & Governance Development FAQs
Pilots and integrations ship in 6–10 weeks. Full-scale platform builds run 12–20 weeks for focused programs and 9–18 months for enterprise GRC modernization. After a 30-minute discovery call, we provide a detailed milestone-driven timeline before you commit.
Both. We build custom cloud-native GRC platforms when off-the-shelf tools don't fit, and we extend ServiceNow GRC, MetricStream, Archer, OneTrust, and LogicGate when those platforms anchor your stack. Most successful programs blend custom AI layers on top of stable GRC cores.
Compliance is engineered, not retrofitted. Every engagement starts with regulatory mapping for your industries and geographies. We build obligation-to-control maps that translate 300+ global frameworks into a unified control library so the same evidence satisfies multiple regulators simultaneously.
Yes. We integrate with SIEM platforms (Splunk, Sentinel), vulnerability scanners, IAM systems (Okta, SailPoint), ticketing (Jira, ServiceNow), HRIS, ERPs, and cloud security posture tools. Compliance evidence flows from operational systems into the GRC layer not collected by hand.
You own 100% of the source code, ML models, control libraries, and documentation from day one. Full IP assignment is signed before sprint one. Your codebase lives in your GitHub organization operable entirely by your team after handoff.
Fixed-scope projects, dedicated teams, nearshore development centers, and time-and-materials. Most compliance engagements run as dedicated teams with fixed milestones. We'll recommend the right model during discovery based on your scope, regulatory calendar, and audit cycles.
As a non-technical founder, building a platform carries enormous risk. ZAPTA understood the challenges growing businesses face and guided us with deep expertise, a great project lead, and out-of-the-box ideas that improved our initial design.
Awards & recognitions


ZAPTA didn't just build what I asked. They challenged my ideas, brought my vision to life from concept to mobile app, and are there whenever I call. They treat VirtuVault like their own business.
Our partners


As a former IT project manager, I know thoroughness when I see it. I bid the development out on several platforms, but ZAPTA's scope was the most thorough I'd ever seen, with a dedicated team and project manager.
Our clients


10 Best Custom Software Development Companies Dominating NYC & the US
What Are the Mistakes Companies Make Before Software Development?